As artificial intelligence becomes increasingly embedded in enterprise technology, one question is becoming harder to ignore: how much authority should intelligent systems actually have?
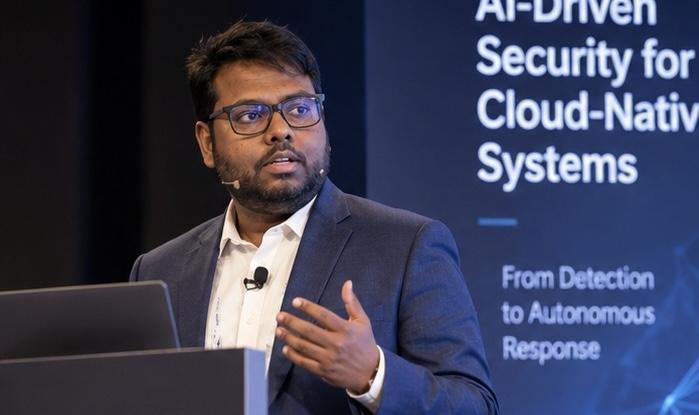
For technology architect, researcher, and AeglysAI creator Shubh Prabhat, the answer is not to place artificial intelligence in unrestricted control of security decisions. Instead, his work explores an architecture in which AI and behavioral analytics provide intelligence about changing risk while deterministic security policies retain authority over what a system is permitted to do.
Prabhat describes this direction as policy-bounded adaptive security, an approach emerging from his years working with distributed systems, cloud platforms, identity, authorization, cybersecurity, and enterprise modernization.
From Static Controls to Changing Risk
Traditional authorization models remain essential to enterprise security. Role-Based Access Control determines permissions through roles, while Attribute-Based Access Control can incorporate additional characteristics of users, resources, and environments.
The challenge, Prabhat argues, appears when the environment changes after those rules have been established.
A valid user may begin a session from an unfamiliar device. Access may occur at an unusual time. Request behavior may suddenly differ from historical patterns. A resource may become more sensitive because of changing operational conditions.
“Identity is an important part of authorization, but identity alone does not describe the complete risk surrounding an interaction,” Prabhat says. “The question is how systems can incorporate changing evidence without turning security policy into an unpredictable black box.”
His research focuses on separating risk intelligence from enforcement authority. Behavioral and operational signals can influence a risk assessment, but predefined policy boundaries determine whether that evidence results in allowing access, requiring additional verification, limiting activity, or denying a request.
Building the Idea Through AeglysAI
Prabhat is exploring this architecture through AeglysAI, an open-source research and engineering initiative focused on adaptive intelligence for secure and resilient distributed systems.
Rather than positioning AeglysAI simply as another AI security product, the initiative is intended as an experimental environment for examining how intelligent capabilities can be incorporated into distributed-system control loops while remaining explainable, observable, and constrained.
The work builds on concepts including Zero Trust, contextual authorization, behavioral risk, distributed systems, identity, and resilient system design.
A central research progression examines increasingly adaptive authorization models—from traditional role-based approaches through attribute and contextual models toward behavioral risk-aware authorization.
The objective is not merely to produce a more complex access-control mechanism. It is to determine whether adaptive approaches can improve security decisions while maintaining properties enterprise systems depend upon: predictability, auditability, reproducibility, and policy compliance.
Explainability as a Security Requirement
One of the difficult questions surrounding AI-assisted security is explainability.
A system that produces a risk score without showing why that score changed may create new operational problems for security teams.
Prabhat’s approach therefore emphasizes decision evidence.
If a system recommends additional verification, for example, engineers should be able to understand whether the decision was influenced by an unfamiliar device, abnormal request frequency, unusual timing, resource sensitivity, or another signal.
“Security teams need more than a number,” he says. “They need to understand what evidence contributed to the decision and which policy ultimately determined the response.”
This separation could also make adaptive systems easier to audit because the intelligence layer and policy-enforcement layer can be examined independently.
Research Beyond a Single Implementation
Prabhat’s broader professional work spans approximately 18 years across software engineering, architecture, cloud-native systems, microservices, identity and authorization, cybersecurity, and enterprise technology.
His current research direction brings several of those areas together around a single question: how can distributed systems become more intelligent without becoming less governable?
Alongside AeglysAI, his research activities include technical publications, peer review, conference participation, and intellectual-property work related to secure and adaptive computing systems.
AeglysAI is also developing a community-oriented engineering program intended to give students, researchers, and engineers opportunities to experiment with adaptive security problems through reproducible technical challenges.
Intelligence Within Boundaries
The future of cybersecurity may involve considerably more automation, but Prabhat believes automation alone is not the goal.
“An intelligent system should be capable of observing changes and assessing risk,” he says. “But intelligence becomes more useful when engineers can define the boundaries within which that intelligence is allowed to operate.”
That principle is summarized in AeglysAI’s engineering sequence:
Observe. Assess. Authorize. Respond.
For Prabhat, the next stage of adaptive security is therefore not about replacing deterministic engineering with AI. It is about determining how the two can work together—using intelligence to understand changing conditions while keeping security-critical authority bounded, explainable, and accountable.
The supporting documentation, system architecture, experimental materials, and implementation artifacts are publicly accessible through the AeglysAI project website and its open-source GitHub repository.